 Matthew Firth · Oct 3, 2026 · 5 min read
"Shadow AI" gets used almost exclusively to describe employees pasting company data into a consumer chatbot nobody approved. That's a real problem, and most organizations now have a policy for it. But running a NIST-aligned security and audit program at OmniMetrix has shown me a sharper version of the same risk, one that doesn't show up in any shadow-IT scan: AI-generated code and AI-assisted engineering decisions entering production without ever passing through the attribution and review trail the compliance program assumes every change takes.
Shadow AI is not just a browser tab
A shadow-IT policy catches the chatbot. It does not catch a developer accepting an AI-suggested function inside their own IDE, inside an approved tool, as part of an approved workflow. Nothing about that looks unauthorized. The commit lands in the same repository, goes through the same CI pipeline, and gets the same green checkmark as code the developer wrote by hand. The audit trail that a NIST-aligned program depends on, who decided what, and why, quietly thins out exactly where AI involvement is heaviest, because nothing in the tooling asks the question.
Treat AI-generated code like an unvetted vendor
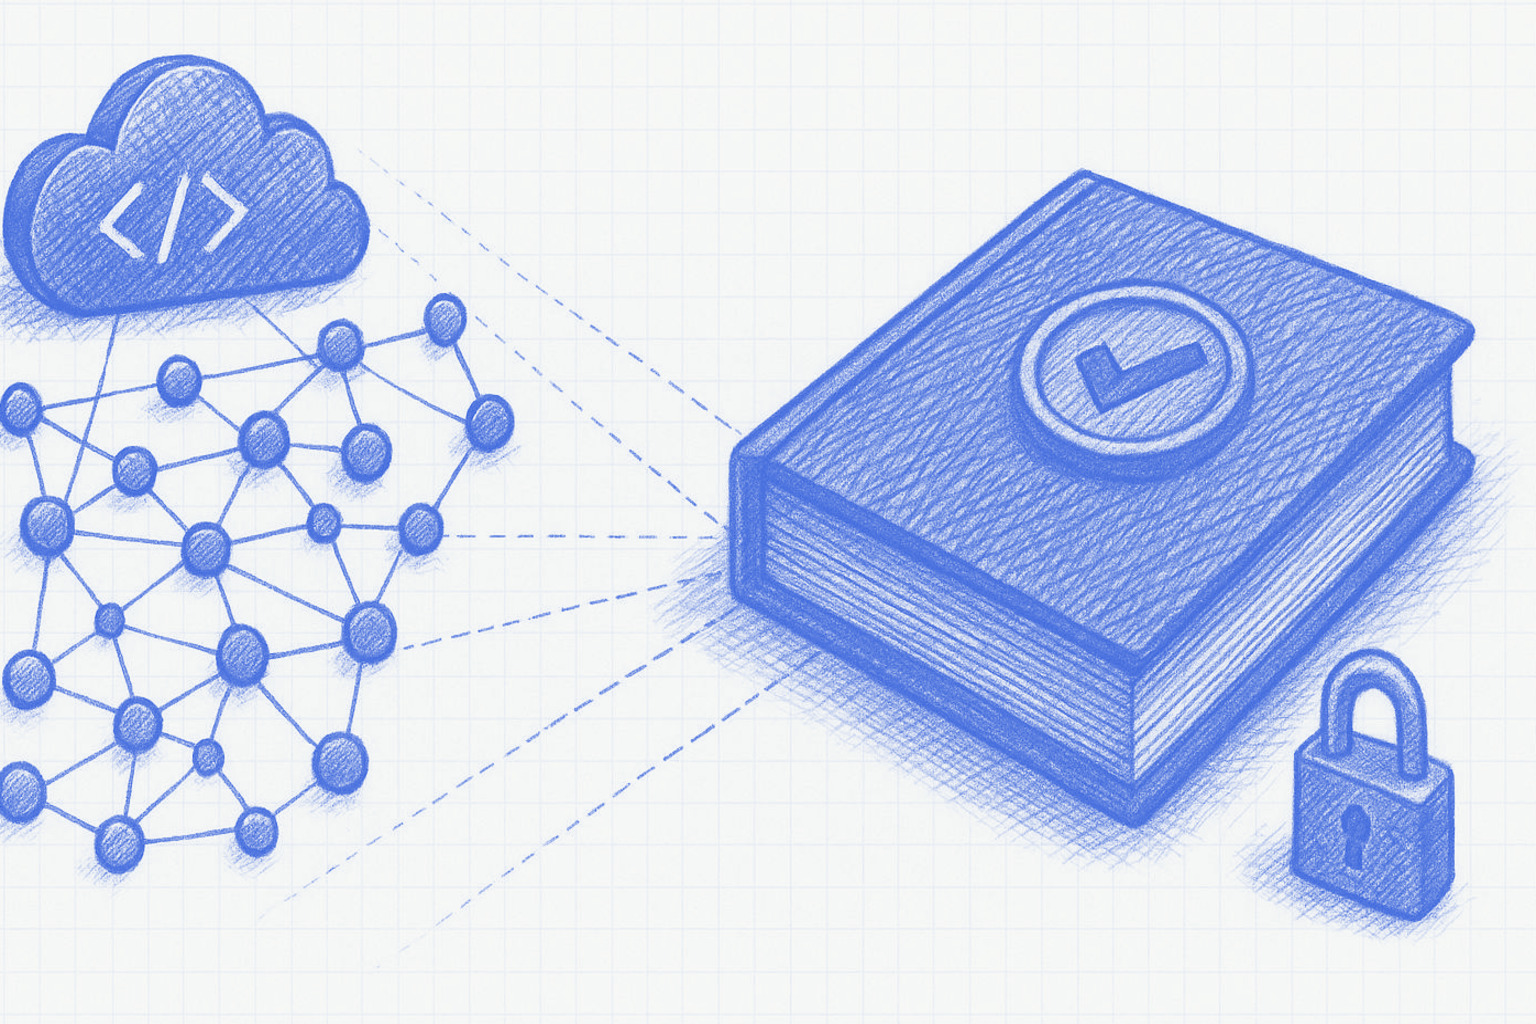
No engineering org I've worked in would let a new third-party package into production without it going through dependency review: license check, known-vulnerability scan, an owner who signed off on taking the dependency on. AI-authored code deserves exactly that level of scrutiny, not a ban and not a shrug. The useful framing isn't "AI wrote this, so it's suspect." It's "this came from outside a human's direct authorship, so it goes through the same gate anything else from outside a human's direct authorship goes through."
AI-authored code deserves the scrutiny we already give a new dependency, not a ban and not a shrug.
Three controls that cost almost nothing
The fix doesn't require new tooling. It requires making three things explicit that most teams currently leave implicit. First, a commit or pull request involving significant AI generation says so, along with which tool or model produced it, the same way we'd note a vendored library's source. Second, that code gets the same human sign-off bar as human-written code; "the AI wrote it and it looked fine" is not a review. Third, when AI materially informs a security or compliance decision, that decision gets the same ticket and audit-log entry a human-made decision would get. None of this slows a team down in any way that matters. It just makes the trail that already exists for every other kind of change exist here too.
This is a governance problem, not a tooling problem
Every security program I've built assumes that important decisions leave a trace someone can later follow. AI assistance doesn't threaten that assumption because the code is worse. Plenty of it is excellent. It threatens the assumption because the normal reasons a trace gets left, a PR description, a design doc, a reviewer's comment, are exactly the steps that feel most optional when a tool produced the first draft in seconds. Closing that gap is a matter of policy and habit, not a new security product, and it's cheaper to fix before an auditor asks the question than after.